Copy and paste operations between the guest operating system and remote console are deactivated by default.
To enable it:
Browse to the virtual machine in the vSphere Client inventory
Right-click the virtual machine and click Edit Settings.
Select Advanced Parameters.
Add or edit the following parameters.
isolation.tools.copy.disable False isolation.tools.paste.disable False isolation.tools.setGUIOptions.enable True These options override any settings made in the guest operating system’s VMware Tools control panel.
Click OK.
(Optional) If you made changes to the configuration parameters, restart the virtual machine.
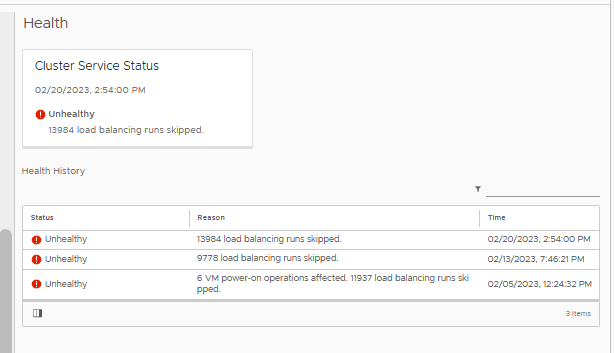
If you see such an error on the Cluster object of a vSAN (in my case it appeared on two vSAN clusters managed by the same vCenter)
vSphere DRS functionality was impacted due to an unhealthy state vSphere Cluster Service …….
an unhealthy state of the Service cluster
Errors such as the following in the EAM log. vCenter LOG
EAM.log:
2023-01-26T13:16:39.996Z |  INFO | vim-monitor | VcListener.java | 131 | Retrying in 10 sec.
2023-01-26T13:16:41.432Z | ERROR | vlsi | DispatcherImpl.java | 468 | Internal server error during dispatch
com.vmware.vim.binding.eam.fault.EamServiceNotInitialized: EAM is still loading from database. Please try again later.
        at com.vmware.eam.vmomi.EAMInitRequestFilter.handleBody(EAMInitRequestFilter.java:57) ~[eam-server.jar:?]
        at com.vmware.vim.vmomi.server.impl.DispatcherImpl$SingleRequestDispatcher.handleBody(DispatcherImpl.java:373) [vlsi-server.jar:?]
        at com.vmware.vim.vmomi.server.impl.DispatcherImpl$SingleRequestDispatcher.dispatch(DispatcherImpl.java:290) [vlsi-server.jar:?]
        at com.vmware.vim.vmomi.server.impl.DispatcherImpl.dispatch(DispatcherImpl.java:246) [vlsi-server.jar:?]
        at com.vmware.vim.vmomi.server.http.impl.CorrelationDispatcherTask.run(CorrelationDispatcherTask.java:58) [vlsi-server.jar:?]
        at java.util.concurrent.ThreadPoolExecutor.runWorker(ThreadPoolExecutor.java:1149) [?:1.8.0_345]
        at java.util.concurrent.ThreadPoolExecutor$Worker.run(ThreadPoolExecutor.java:624) [?:1.8.0_345]
        at java.lang.Thread.run(Thread.java:750) [?:1.8.0_345]
2023-01-26T13:16:50.007Z |  INFO | vim-monitor | ExtensionSessionRenewer.java | 190 | [Retry:Login:com.vmware.vim.eam:b55a7f93b59f0f7e] Re-login to vCenter because method: currentTime of managed object: null::ServiceInstance:ServiceInstance failed due to expired client session: null
2023-01-26T13:16:50.007Z |  INFO | vim-monitor | OpId.java | 37 | [vim:loginExtensionByCertificate:913aec585658e328] created from [Retry:Login:com.vmware.vim.eam:b55a7f93b59f0f7e]
2023-01-26T13:16:51.440Z | ERROR | vlsi | DispatcherImpl.java | 468 | Internal server error during dispatch
com.vmware.vim.binding.eam.fault.EamServiceNotInitialized: EAM is still loading from database. Please try again later.
And you see the lack of vCLS VMs in the two vSANs
To resolve the anomaly you must proceed as follows:
vCenter Snapshots and Backup
Log in to the vCenter Server Appliance using SSH.
Run this command to enable access the Bash shell:
shell.set --enabled true
Type shell and press Enter.
Run this command to retrieve the vpxd-extension solution user certificate and key:
Note: If this produces the error “Hostname mismatch, certificate is not valid for ‘localhost'”, change ‘localhost’ to the FQDN or IP of the vCenter. The process is checking this value against the SAN entries of the certificate.
Note: The default user and domain is Administrator@vsphere.local. If this was changed during configuration, change the domain to match your environment. When prompted, type in the Administrator@domain.local password.
Restart EAM and start the rest of the services with these commands:
Well, in recent weeks we have often talked about how to heal vCenters from the log4j vulnerability. I guess the first thing we all thought was “What a show VMware support released scripts to run to solve the problem …” and then every one to use WinSCP or similar tools/commands to copy the file …. but many will have found it impossible to copy files using the Root user …. but how SSH works but the SCP command does not work! Well, the problem comes from the shell associated with the Root user. It is not the classic BASH but the APPLIANCESH. Then we proceed as follows:
Let’s connect in SSH to the vCenter Virtual Appliance
We access the Bash SHELL with the command SHELL
We enable BASH as the default shell for the root user
Whenever we installed a new vCenter the activity always included integration with Active Directory and normally IWA (Integrated Windows Authentication) was used. Since vSphere 7.0 version this possibility has been deprecated so it is good to start with the integration of the vCenter with Active Directory via LDAP. In our case, we will use LDAPS which uses a certificate
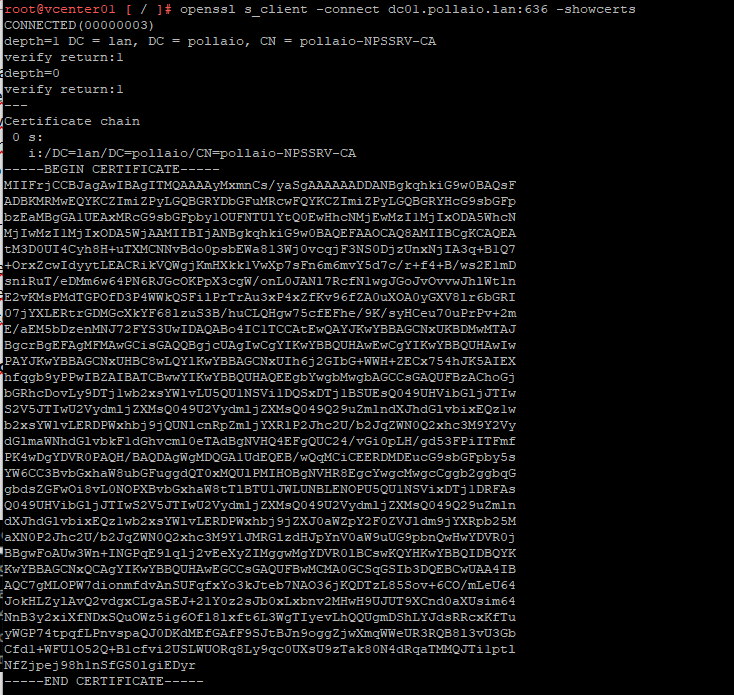
For first the step we need to create the certificate:
Copy the certificate output with —–BEGIN CERTIFICATE—– and —–END CERTIFICATE—–
Past on Notepad and save with .crt extension
Now we will go to configure the Identity Sources on vCenter:
Login as Single Sign-On Administrator to vCenter
Navigate to Menu > Administration > Single Sign-On > Configuration
In the Identity Provider tab, open Identity Sources
Click ADD
Select Active Directory over LDAP or OpenLDAP, depending on your directory type.
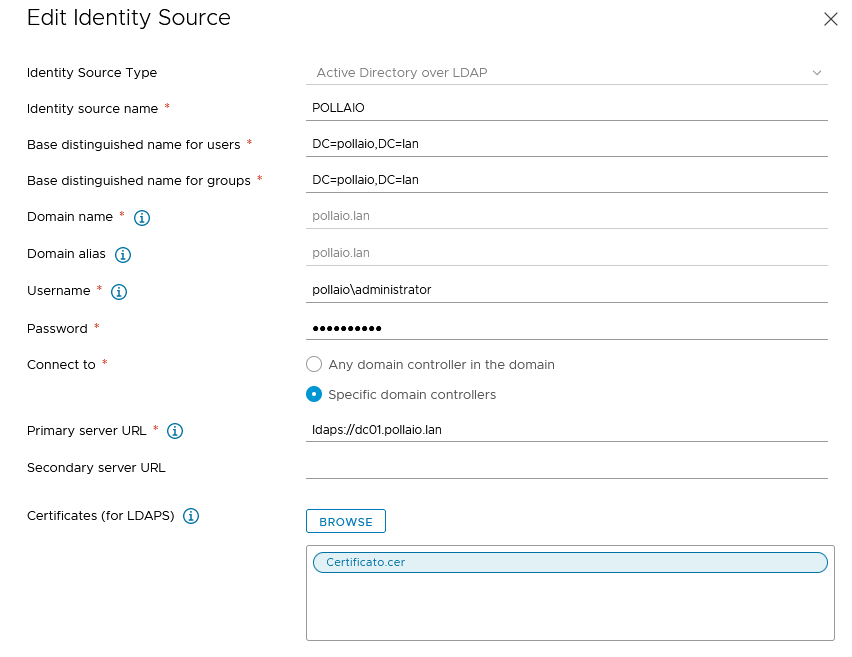
Fill out the remaining fields as follows: Identity Source Name: Label Base DN for users: The Distinguished Name (DN) of the starting point for directory server searches. Example: “DC=pollaio,DC=lan”. Base DN for groups: The Distinguished Name (DN) of the starting point for directory server searches. Domain name: Your domain name. Example: “pollaio.lan” Domain alias: Your NetBIOS name. Example: “pollaio.lan” Username: Domain user with at least browse privileges. Example: “pollaio\administrator”. Connect to: “ldaps://<DC FQDN>”.
Click Browse next to SSL Certificate
Select the .cer file created in before step
Now we are ready to login to the vCenter with domain user (remember to assign the correct permission to domain group or user group)
If you want check the correct use of SSL certificate on the authentication to Active Directory with LDAP connection check the websso.log:
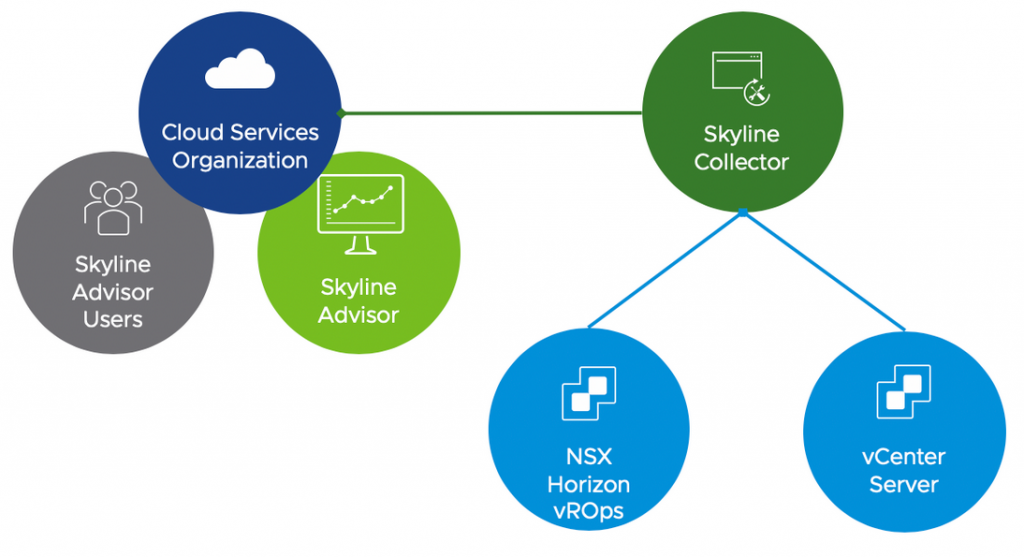
VMware has had a product for a while now called VMware Skyline that provides proactive monitoring, analysis, and support for your VMware environment. It monitors your VMware installation and will notify you when issues arise.
Skyline Advisor will be available to customers and partners with active Production and Premier Support, VMware Success 360 and vRealize Cloud Universal subscriptions at no additional cost.
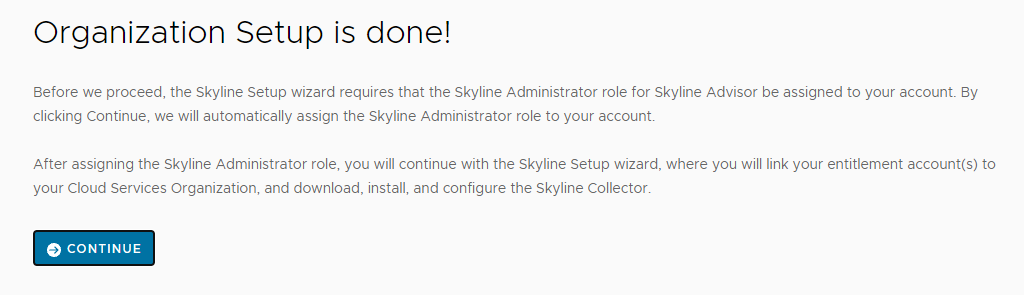
Create a Cloud Services Organization
Login with My VMware account associate to Production and Premier Support on the site:
https://console.cloud.vmware.com/
After clicking Get Started, a new web browser page, or tab, will open. You will be asked to sign-in
with your VMware account. If you have an existing My VMware account, you can use those same
account details (email address/password) to sign in to Cloud Services.
If you are existing VMware Cloud Services customer, you can choose an existing Cloud Services
Organization for Skyline. If you have never used VMware Cloud Services, click Create New
Organization.
Enter a Organization Name.
Name your Organization something meaningful, that can be easily
referenced by both you, and VMware. For example, name your Organization after you Company, or
Business name. You can also append a line-of-business, division, or team, to the end of your
Company or Business name.
The following are example Organization Names:
The company, LOB, Company LOB, Company-vSphere, Company-Desktop
Enter an Address for your Organization.
Click Add Address. You can also choose an existing
address if one was found for your account. If you choose an existing address, skip to substep f.
During the creation of your Cloud Services Organization, your country currency, and Tax ID, may be
displayed. The displaying of this information is a construct of Cloud Services. Skyline is available at
no additional cost, and you will not be required to enter any payment details while adopting Skyline.
Select a Country from the drop-down menu.
Enter your street address on Address Line 1, and Address Line 2 (optional).
Enter your City.
Enter your State/Province.
Enter your Zip/Postal Code.
Review the Cloud Services Terms of Service. Click the checkbox to agree to the Terms of Service.
Click Continue.
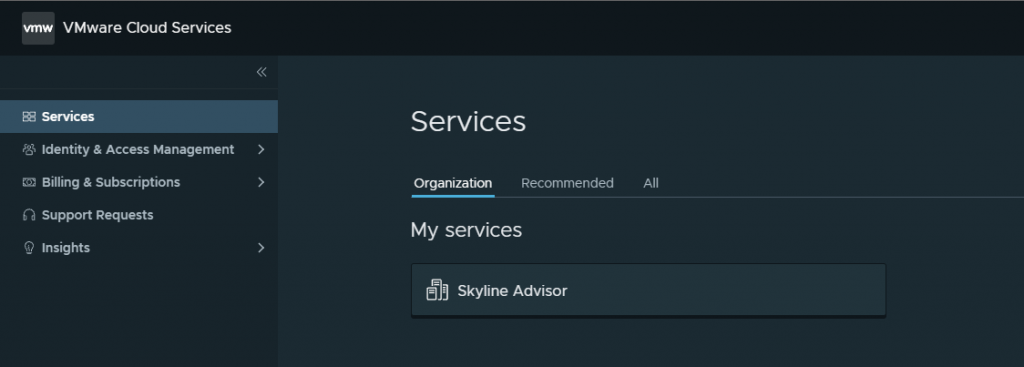
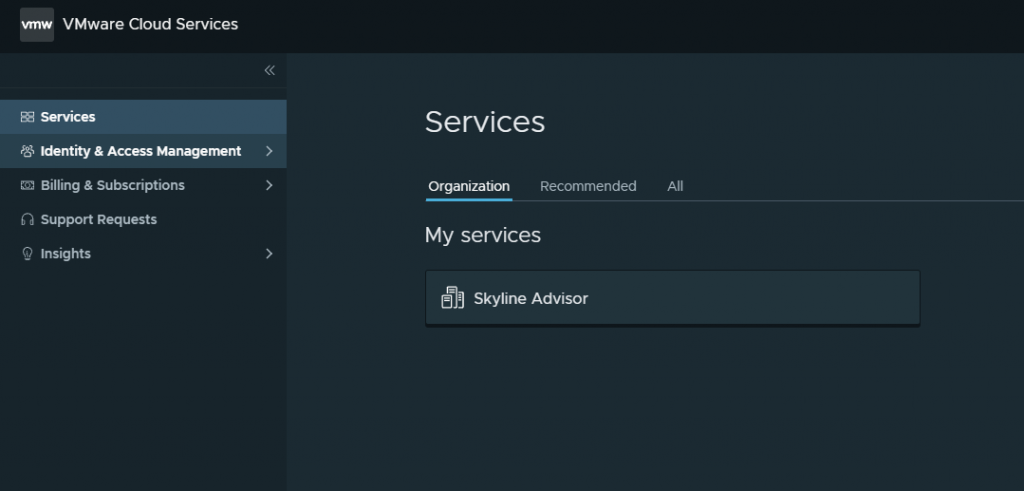
Now on service, we have Skyline Advisor, click on this service
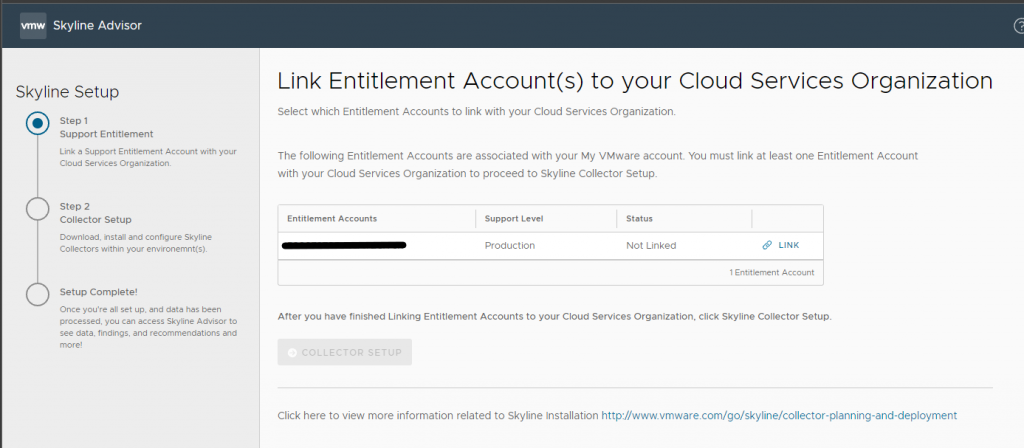
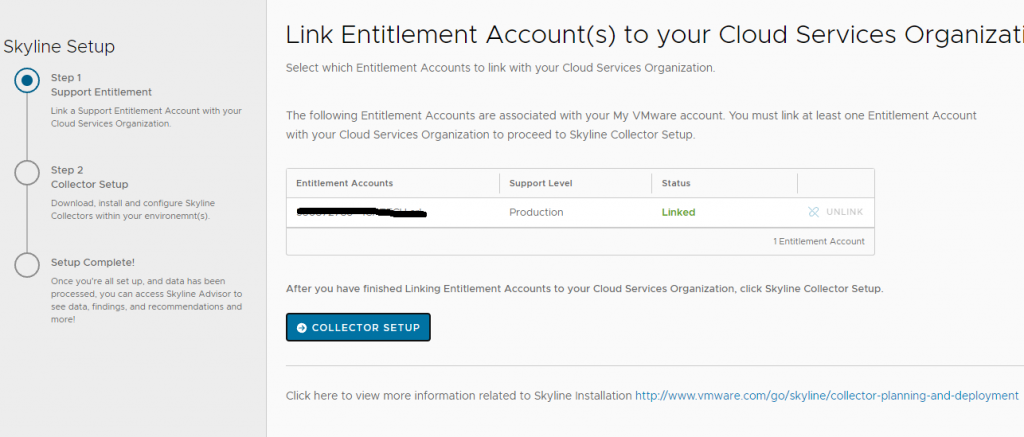
Link the Entitlement
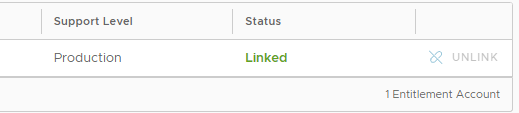
Now, after clicking on LINK, we have the correct status LINKED
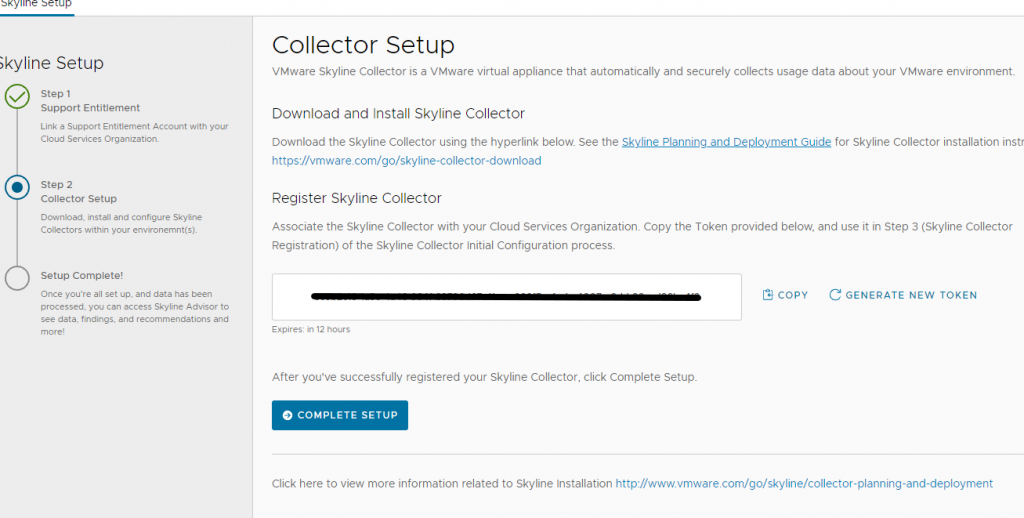
Deploy Skyline Collector and configure the connection to Cloud Services
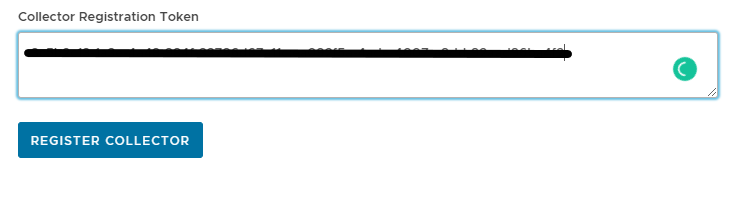
Copy and paste the token on Skyline Connect and register it.
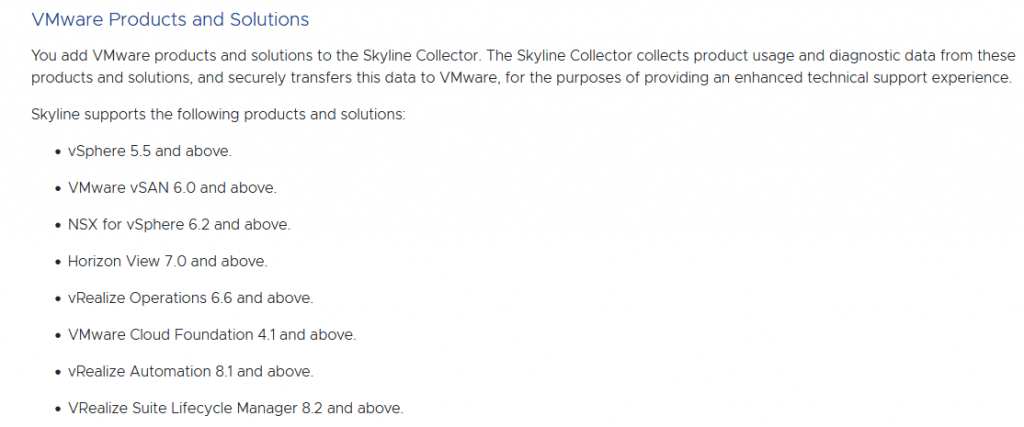
Add source Data to Skyline Advisor
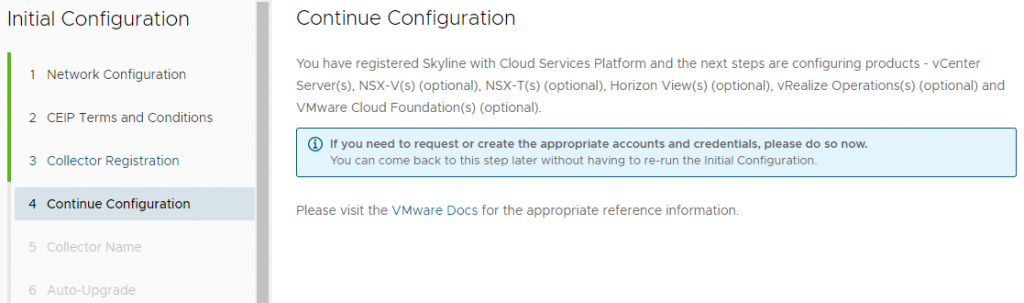
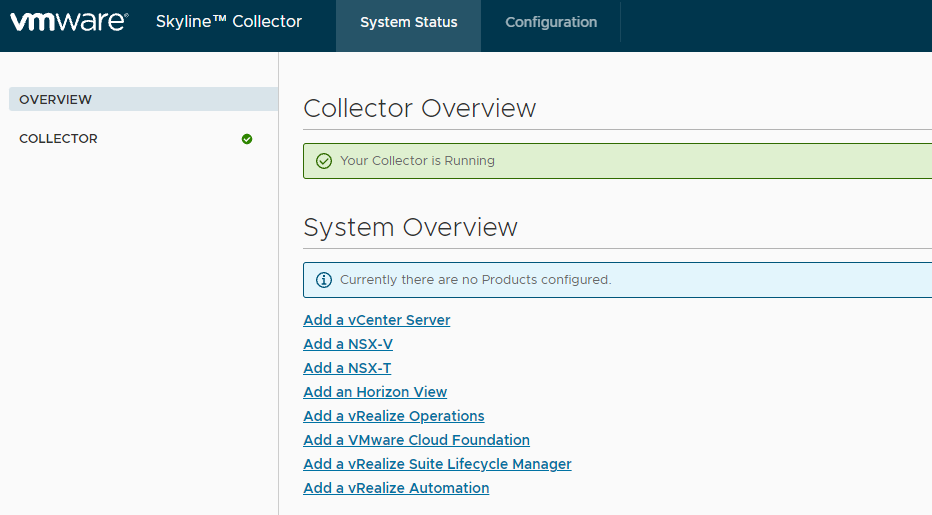
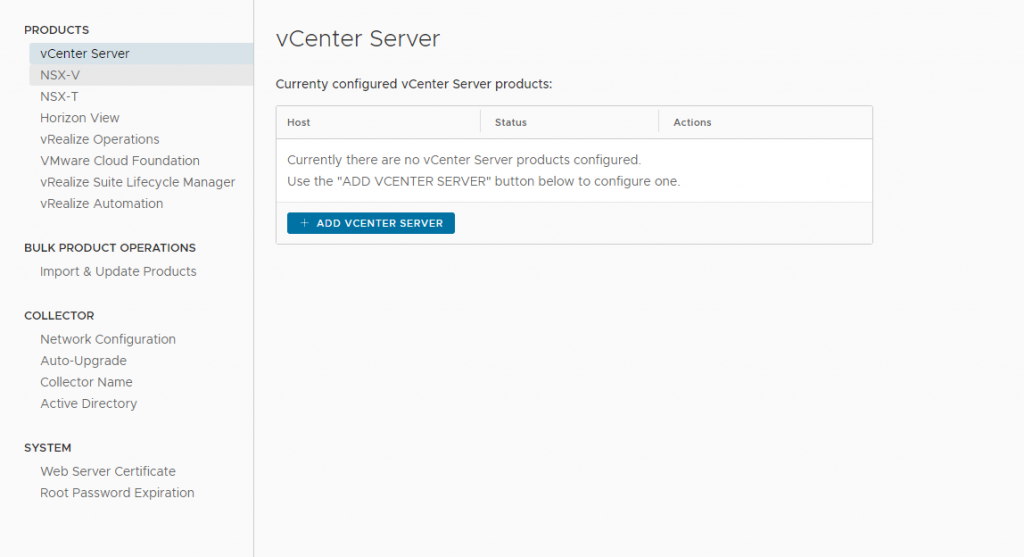
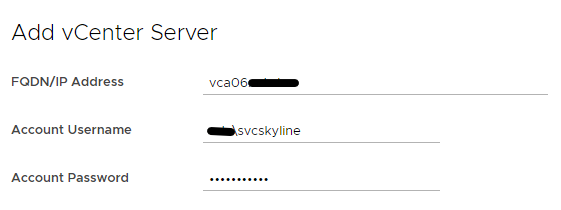
After complete the step 5 and 6 (I suggest to enable the auto-upgrade), we can access to skyline collector to configure the connection to vCenter (or multiple vCenter)
One of the conveniences of administering VMware solutions is being able to use code to create scripts to perform repetitive tasks or automate processes
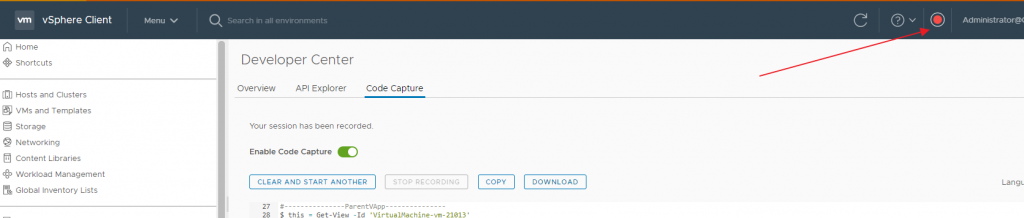
One of the vSphere Web Client features that can help those new to the PowerCli is the Capture Code, it basically allows you to list and save the Powercli commands of the actions you are doing with the vSphere Web Client.
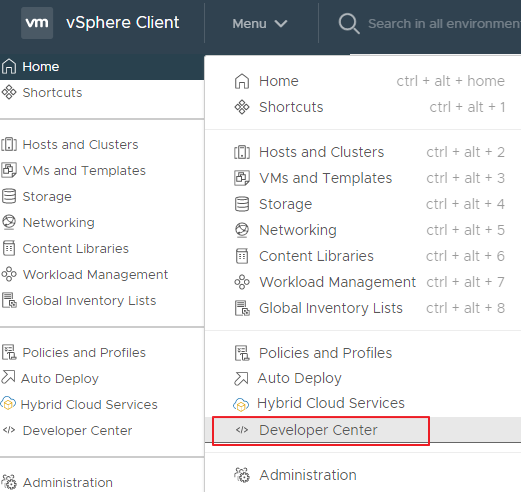
To activate it just access the vSphere Web Client, from the Menu select Developer Center
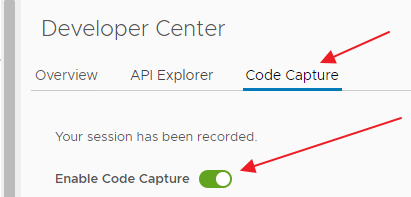
Select Code Capture and enable it by placing the “Enable Code Capture” flag on the right (which turns green)
At this point, a space will appear in our frame where the commands will be listed with some operations, such as Clear and start another, Copy and Download
Where the Download option generates you the ps1 file with the Powercli commands of the recorded operations
To start and stop a recording session you can use the buttons:
Or the red button that appears at the top of the WebClient once “Enable Code Capture” is enabled
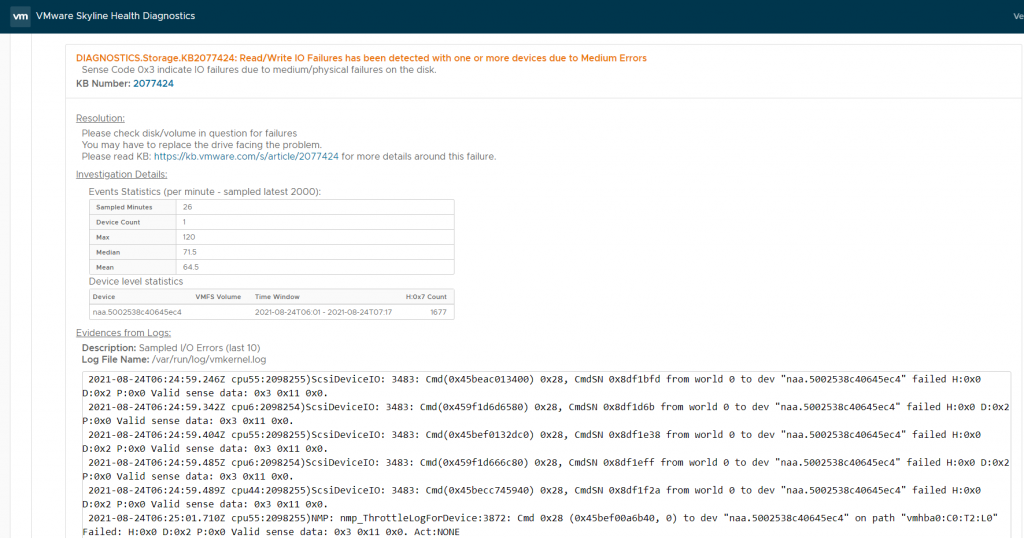
Imagine you have a vSAN infrastructure and at some point, a diskgroup fails but errors are reported on the disks. With this tool, we can analyze the logs exported from the ESXi host on which the diskgroup resides and identify on which physical disks I / O errors have been highlighted
vSphere use TLS Certificates for protect and security communication from vCenter to ESXi host and when the user access to vCenter WEB GUI.
There are many possible configurations:
Full Managed Mode -> All certificates are managed from VMCA
Hybrid Mode -> The communication certificates for traffic from vCenter to ESXi are managed from VMCA. The Admin user import from Private PKI only the SSL certificate for Access to WEB GUI
Subordinate CA Mode -> Configure the VMCA as a Subordinate CA of Private PKI
Full Custom Mode –> All Certificates are generated and managed from the local Private PKI
The best solution is Hybrid Mode for correct balance of Security and effort for implementation.