SaaS License Activation for Omnissa Horizon without EDGE Gateway

In the latest versions of Horizon, it is recommended to use the SaaS subscription, which requires the installation of an EDGE Gateway component generated by the Omnissa Connect portal under Horizon in the customer section.

This involves the need to install a Linux VM on our vSphere environment; not for everyone is this feasible:

–Need not have connections with Cloud services
–Resource savings (CPU, RAM and disk space)
–Test environments and any POCs
–Or, as in my case, I must test the new versions of Horizon

For this last point and since I need to install version 2606 as a test, I decided to explain how to do it… step by step.

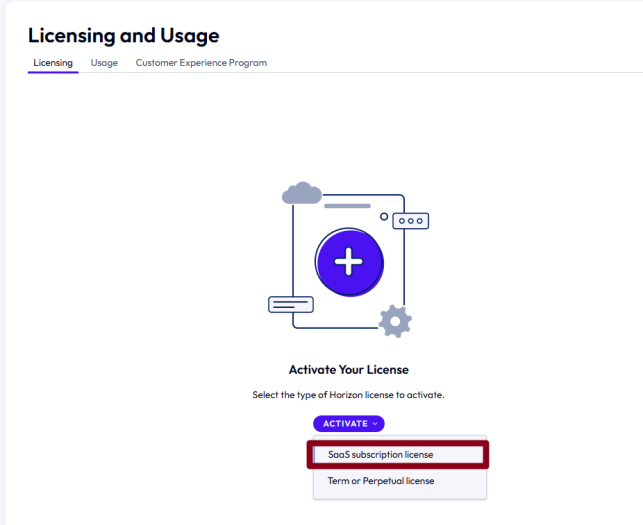
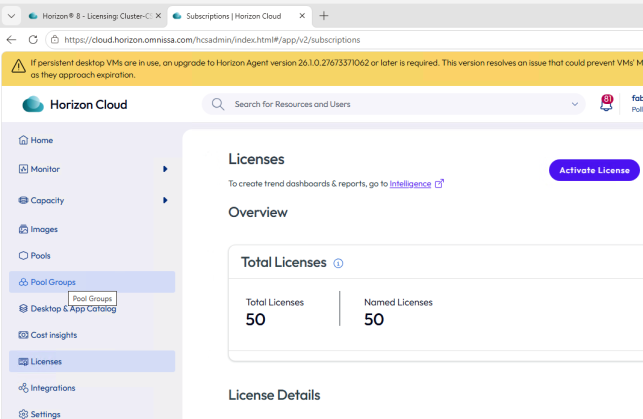
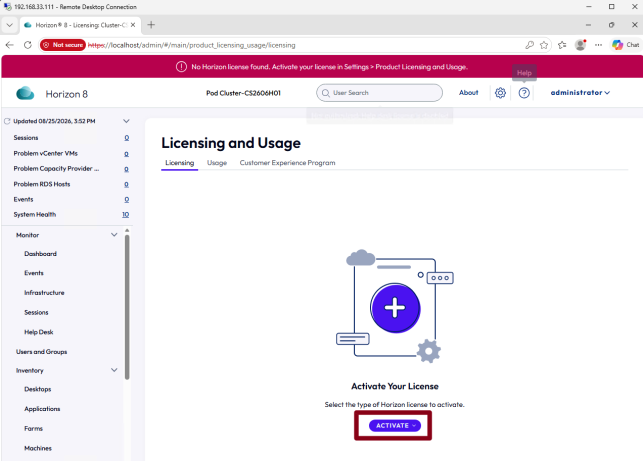
Installed my connection server on a Windows Server 2025. The first thing to do is access the administration console and activate the license:

.

.

.

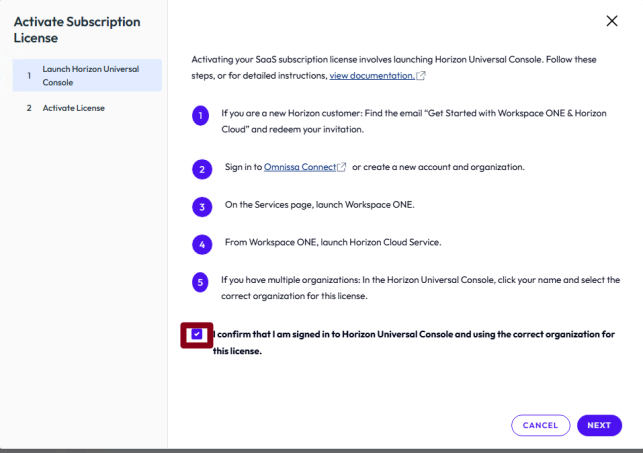
Verify that you have received the activation email or that you have a Horizon SaaS subscription and that you have access to the Connect Omnissa portal

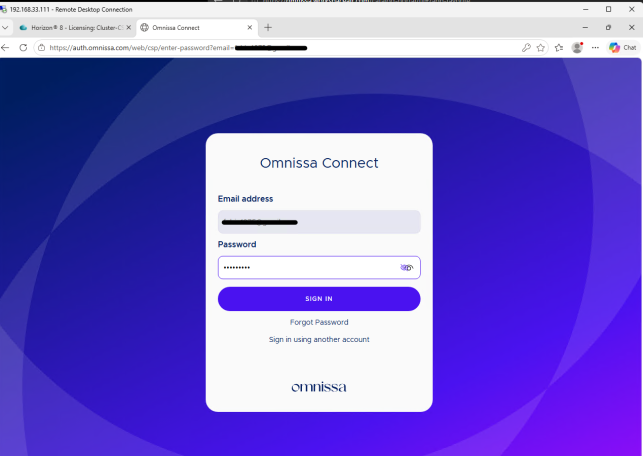
So you must log in to the Omnissa Connect portal (by opening a TAB from the Browser you are using to access the Horizon console) and authenticate on connect.omnissa.com and keep the tab open.

.

.

Enter accounts, passwords and if necessary, do MFA

.

.

A new tab will automatically open with the login already made

.

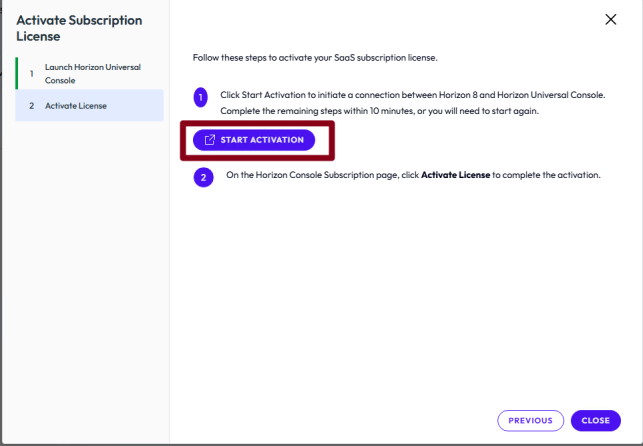
Now run

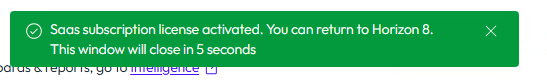
The following message will appear

.

.

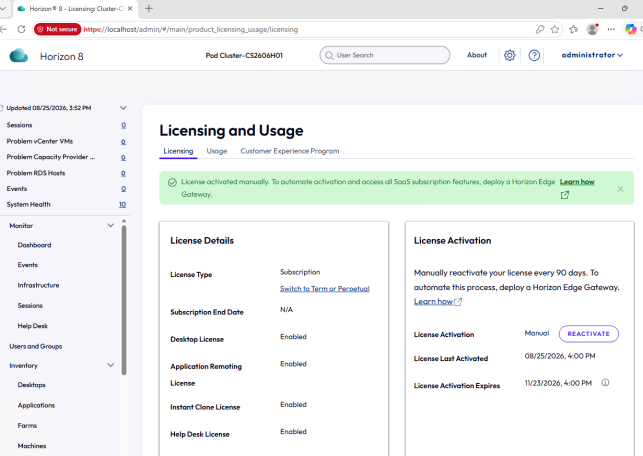
And on the Horizon console, the license status will be as follows

.

.

Two important points

–Mark your calendar to reactivate your license (in the same way) before 90 days have passed
–You can switch to a license via the EDGE Gateway by simply installing the EDGE Gateway (Follow the specific procedure)

.

.

.

.

SaaS License Activation for Omnissa Horizon without EDGE Gateway

Replacing the Self-Signed Certificate on Omnissa Connection Server with a Microsoft CA-Issued Certificate (or replacing the certificate to end to validation date)

.

Let’s be honest — that shiny self-signed certificate your Omnissa Connection Server came with is fine… until your browser or Horizon client starts screaming “Untrusted!” at every login. 😅

A screenshot of a computer error AI-generated content may be incorrect.


It’s time to fix that properly — by replacing it with a trusted certificate issued by your internal Microsoft CA.

In this guide, we’ll walk through the process step-by-step, ending up with a PFX certificate you can deploy to all your Connection Servers.

.

Why One Certificate for All Connection Servers?

Because simplicity is beautiful.
Maintaining a single certificate across all your Connection Servers reduces management overhead and avoids those awkward “name mismatch” warnings.

In the certificate, we’ll include all relevant hostnames as Subject Alternative Names (SANs):

• The hostname and FQDN of each Connection Server
• The VIP name (if you’re using a load balancer for internal access)

Example SAN list (2 Connection Servers and 1 VIP):

connection01.company.local

connection02.company.local

horizon-vip.company.local

connection01

connection02

horizon-vip

.

.

Step 1: Require the certificate as a PFX File

1. The certificate will be exported into a PFX file with:
◦ Exporting the private key
◦ Protect it with a strong password
◦ Save it somewhere safe (seriously, treat it like a password)

.

Step 2: Deploy the Certificate on All Connection Servers

Now that you have your shiny, trusted .pfx file, it’s time to put it to work.

Repeat the following steps on each Connection Server:

1.Open MMC → Certificates (Local Computer) again.
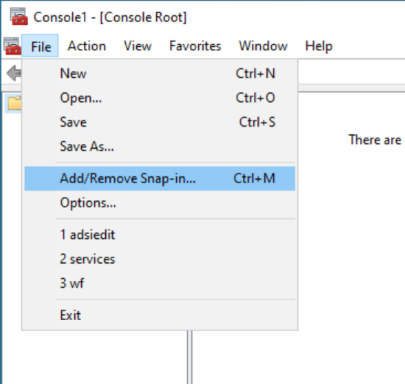
A screenshot of a computer AI-generated content may be incorrect.

A screenshot of a computer program AI-generated content may be incorrect.

A screenshot of a computer AI-generated content may be incorrect.

A screenshot of a computer AI-generated content may be incorrect.

A screenshot of a computer AI-generated content may be incorrect.

In Personal, there is a self-signed certificate (or an old certificate) installed by the Connection Server installation process
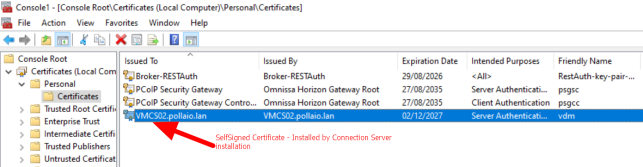
A screenshot of a computer AI-generated content may be incorrect.

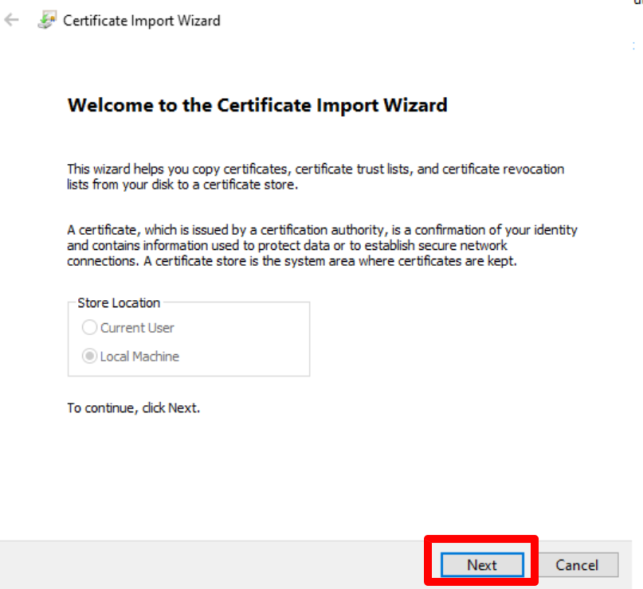
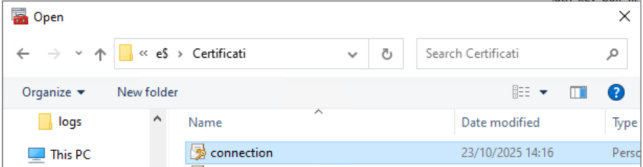
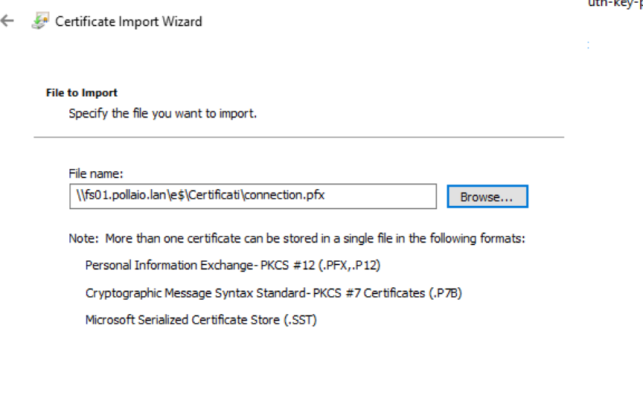
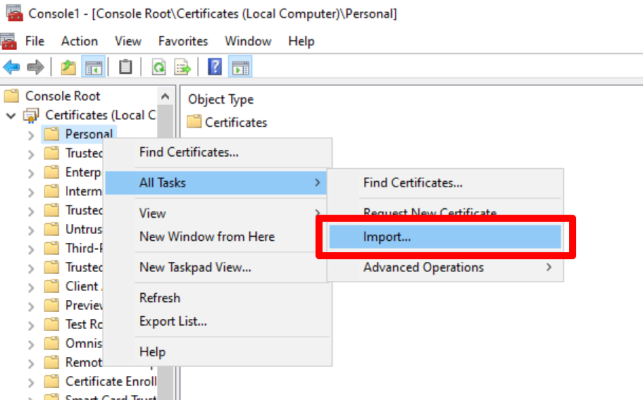
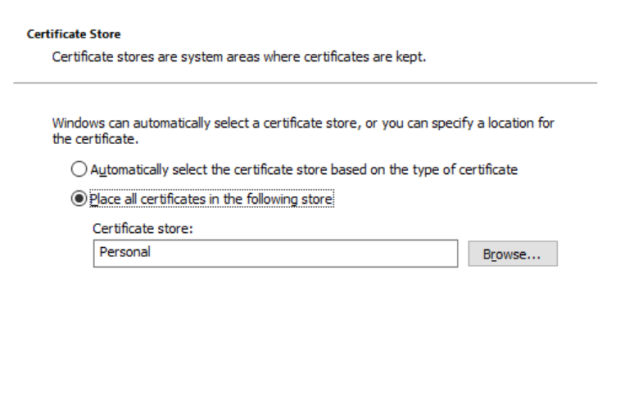
2. Import the .pfx file under:

Personal > CertificatesA screenshot of a computer AI-generated content may be incorrect.
.

A screenshot of a certificate AI-generated content may be incorrect.

A screenshot of a computer AI-generated content may be incorrect.

A screenshot of a computer AI-generated content may be incorrect.

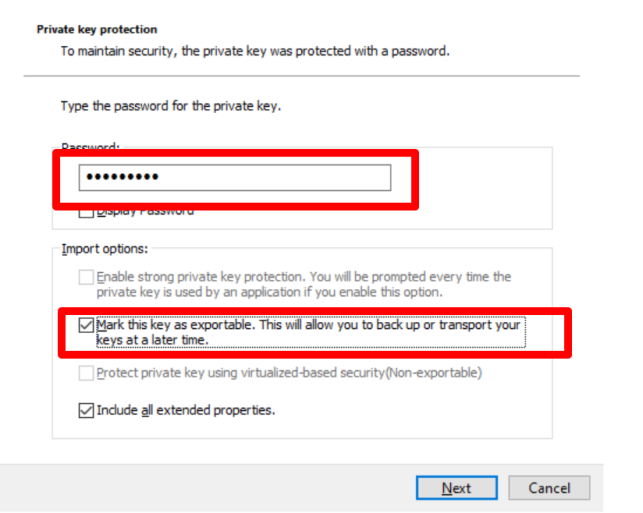
3. When prompted, provide the password you used during export and select “Mark this key as exportable….”
A screenshot of a computer screen AI-generated content may be incorrect.

A screenshot of a certificate AI-generated content may be incorrect.

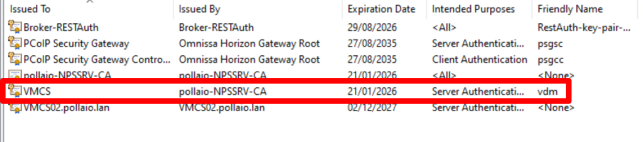
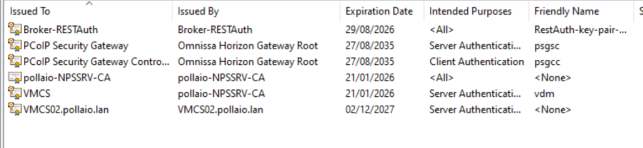
4. Verify that the certificate appears in the list with the private key (the certificate icon has a key)
A screenshot of a computer AI-generated content may be incorrect.

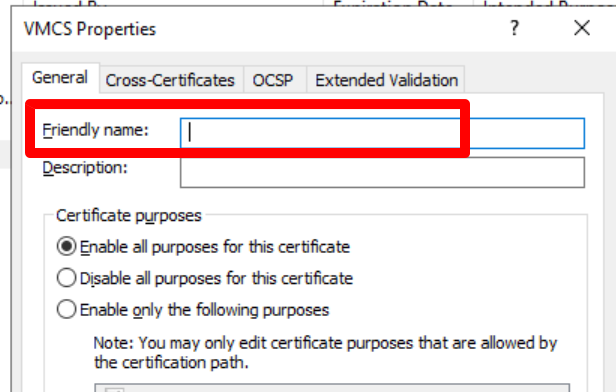
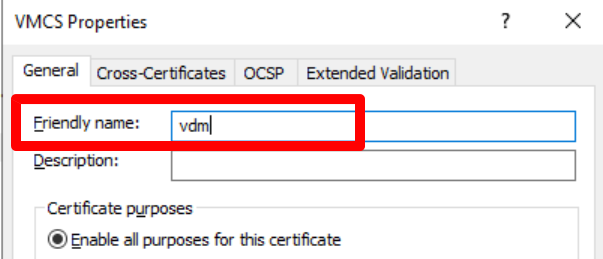
5. Remove the friendly name VDM from the self-signed certificate or the old certificate
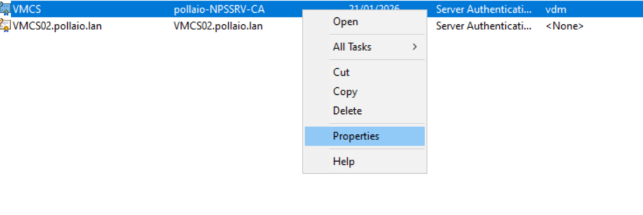
A screenshot of a computer AI-generated content may be incorrect.

A screenshot of a computer AI-generated content may be incorrect.

6.Add friendly name VDM to new certificate
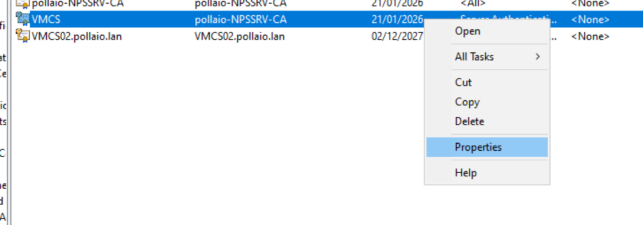
A screenshot of a computer AI-generated content may be incorrect.

A screenshot of a computer AI-generated content may be incorrect.

A red lines with black text AI-generated content may be incorrect.

.

.

Step 3: Restart the Horizon Connection Server Service

To make the change effective:

1. Open Services.msc
2 . Restart the VMware Horizon Connection Server service.
3 . Alternatively, you can simply reboot the server if you’re feeling extra cautious.
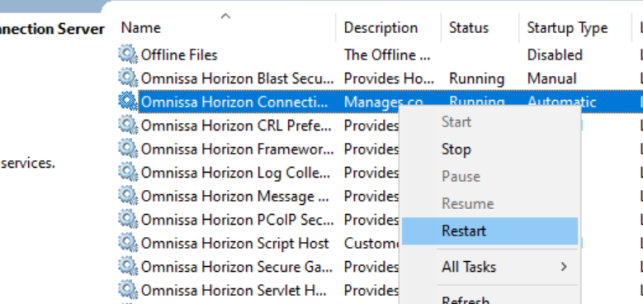
A screenshot of a computer screen AI-generated content may be incorrect.

Once restarted, the Connection Server should automatically pick up the new certificate.

You can confirm by opening the Horizon Administrator Console in your browser and checking that your connection is now secure and trusted ✅

We need to repeat steps 4 and 5 on all Omnissa Connection servers
.

Bonus: Keeping Things Clean

• Make sure all old or expired certificates are removed from the Personal store.
• Keep a note of the certificate expiration date and plan your next renewal ahead of time (trust me, future-you will thank you).
• If the Horizon is behind the Unified Access Gateway (for external connection and network segmentation, remember to change the Thumbprint on the UAG configuration)
IMPORTANT: Once you’ve changed the certificate, always verify that it works. Especially if you have thin clients, make sure they have loaded the necessary certificates (RootCA and SubCA) to validate the new certificate.

.

Done!

You’ve successfully banished the self-signed gremlin and brought your Horizon environment into the trusted world of PKI.

From now on, your users will enjoy clean, warning-free connections — and your security team will silently thank you for doing things the right way.

.
Replacing the Self-Signed Certificate on Omnissa Connection Server with a Microsoft CA-Issued Certificate (or replacing the certificate to end to validation date)

How to test communication between UAG and CS

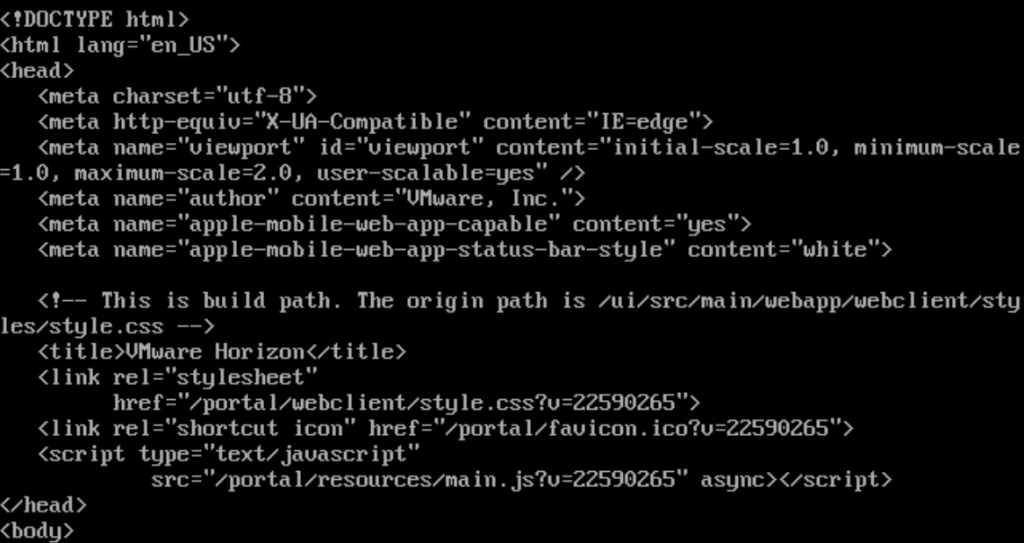
Many times I found myself having to demonstrate that the communication between the Unified Access Gateway and the Connection Servers was not working due to problems with poorly configured firewall rules. A very useful test is to connect to the UAG console and launch the classic CURL command:

curl -v -k https://<FQDN or IP ADDRESS CS>:443/

the outcome of which is as follows if the connection is ok (HTML output)

or the following if the connection is not enabled on the firewall

More info and tools here:

https://docs.vmware.com/en/Unified-Access-Gateway/2309/uag-deploy-config/GUID-390D3A2A-0CB7-4A82-9B0F-D525B74CF55B.html

How to test communication between UAG and CS

421 Unknow

After upgrading Horizon to 2306 2212.1 or 2111.1 we see this message when trying to connect from UAG

In the log, I see this error:

2021-09-24T22:05:34.737-07:00 ERROR (1B08-1A58) <SimpleDeamonThread> [h] (ajp:admin:Request190) Unexpected Origin: https://newname.net

2021-09-24T22:05:34.738-07:00 DEBUG (1B08-1A58) <SimpleDeamonThread> [v] (ajp:admin:Request190) Response 404 Not Found [close]

The fast solution is to set allowUnexpectedHost to true on the locked.properties file. This is located on each connection server in     c:\program files\vmware\VMware View\Server\sslgateway\conf. and restart the horizon connection services

Cross-Origin Resource Sharing (CORS) with Horizon 8 and loadbalanced HTML5 access. (85801) (vmware.com)

Error 421 while connecting to Horizon via HTML Web Console after an upgrade to 2306,2111.1 or Later (93915) (vmware.com)

421 Unknow